<img height="1" width="1" style="display:none;" alt="" src="https://px.ads.linkedin.com/collect/?pid=2740041&amp;fmt=gif">

Security & Operations

AI Compliance

    Discover Can Do

    Explore the platform for project and multi-project management in a personal demo.

    Book a personal demo

      User Perspectives

      User Benefits

        Stay Up to Date

        Newsletter

          What Sets Us Apart

            Take the First Step Towards Greater Efficiency

            Curious whether Can Do meets your requirements? Book a personal meeting and let’s find out together.

            BOOK A PERSONAL DEMO

                Trustworthy AI with Can Do 

                Can Do combines powerful AI with data protection, information security, transparency and clear human oversight. Our architecture and development principles are guided by the regulatory requirements of the EU AI Act, providing a foundation for secure, controlled use of AI across your business.

                For us, AI Act Readiness is part of comprehensive AI governance, rather than a standalone feature.

                  Use AI securely, with control and compliance built in. 

                Book a demo   Watch introduction (German)

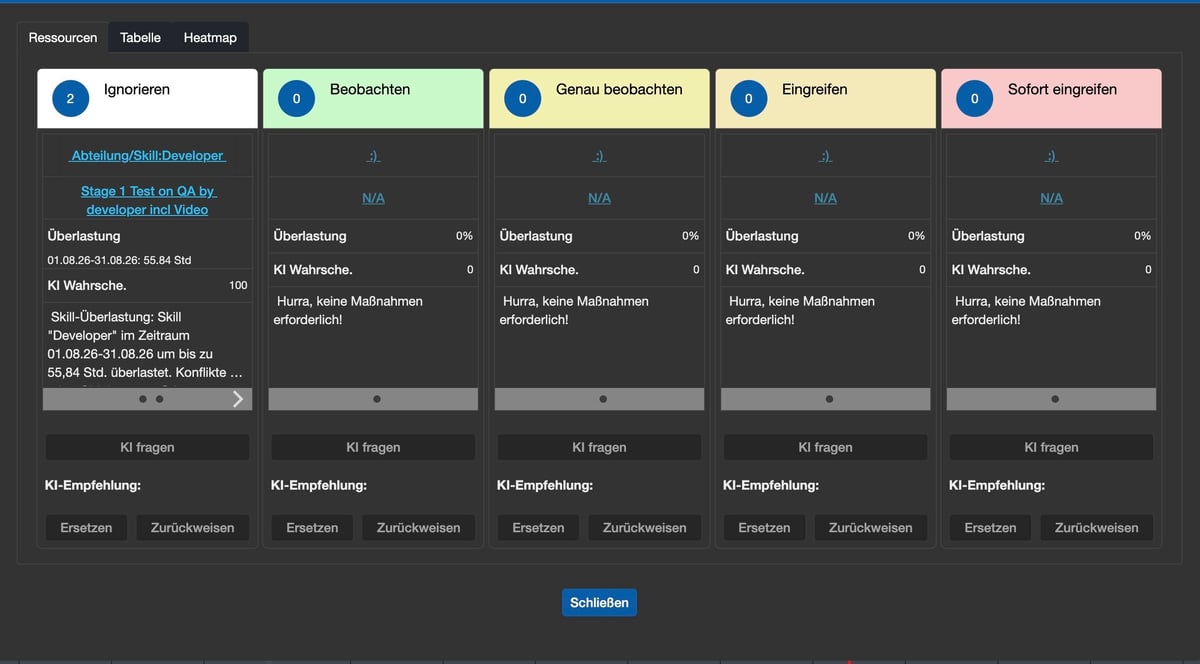
                Can Do resource and project management software (German interface)


                AI in project management needs more than good algorithms

                Artificial intelligence opens up new possibilities in project and resource management. It can identify risks early, predict resource bottlenecks, suggest alternatives and help project managers make complex decisions.

                These possibilities come with greater responsibility. Businesses need to understand how AI reaches its results, what data it processes, who can access that data and how its use can be controlled.

                AI ACT READINESS

                What does AI Act Readiness mean at Can Do?  
                Can Do AI Act Readiness

                The EU AI Act establishes a comprehensive European legal framework for the use of artificial intelligence. It takes a risk-based approach: the greater an AI system’s potential impact on people and businesses, the higher the requirements for transparency, oversight, documentation and risk management.

                Can Do takes these requirements into account when developing and operating its AI-supported features.

                For us, AI Act Readiness means:

                • AI supports people while keeping them in control of decisions.
                • AI models and customer data remain within each organisation’s system environment.
                • Customer data is not sent to public or third-party AI services for analysis and cannot be viewed by Can Do.
                • Access to information is governed by roles and permissions within Can Do, using the settings already in place for each customer.
                • Changes and actions remain traceable.
                • Data protection and information security are integral to the system architecture.
                • AI features are integrated into existing project and resource management processes in a controlled and responsible way.

                Please note: ‘AI Act Ready’ describes how Can Do aligns with the requirements and principles of the EU AI Act relevant to the software. It is not an official European Union certification or seal of approval. A business’s specific obligations also depend on how it uses AI.
                TRUSTWORTHY AI

                Our principles for trustworthy AI

                1. Human oversight & decision-making authority

                Can Do uses AI to support better decisions while preserving human responsibility.

                For example, AI analyses project situations, identifies risks and resource bottlenecks, and suggests suitable alternatives. Users decide which actions to take.

                This combines the power of automated analysis with a central governance principle:

                AI advises. People decide.

                2. Transparency and traceability

                Trust in AI depends on users being able to interpret, review and understand its results, rather than on how many decisions an algorithm can take over.

                Can Do identifies risks and recommends actions while showing the underlying project situation in the context of the plan. Project managers can see where action is needed and make their own informed decisions.

                This creates an important foundation for responsible AI use: Automation while staying in control.

                3. Your data stays yours 

                Can Do’s AI architecture differs fundamentally from many globally operated AI services.

                All learning takes place within each customer’s instance. The neural network learns only from the behaviour of users in that organisation. Learned patterns are neither pooled centrally nor exchanged between Can Do instances.

                Can Do itself does not, as a matter of principle, access customer data or the learning models derived from it.

                No central data collection. No training across organisations. No sharing with public AI systems.

                Your organisation’s knowledge stays where it belongs: in your own system.

                4. Data protection by design

                AI needs data. Data protection therefore needs to be built into the architecture and operations from the outset.

                Can Do is fully GDPR-compliant and offers several deployment options.

                The SaaS version runs on Amazon Web Services (AWS), with servers in Frankfurt am Main or in the region requested by the customer. Redundant systems also operate within the European AWS region.

                Alternatively, Can Do can run on premises in your own data centre or in a private cloud.

                Businesses can choose the deployment model that meets their data protection, security and governance requirements.

                 5. Role-based access control 

                Not every user needs access to the same information.

                Can Do provides technical and content-level access controls. Roles and permissions determine which data users can access.

                This also applies to AI-supported features: users only receive information they are authorised to access within the system.

                AI-supported analyses respect existing permissions.

                6. Audit trails and auditability 

                Governance requires decisions and changes to remain traceable.

                Can Do records changes and actions within the system in a complete, auditable trail. Data and processing steps can be traced, providing a reliable foundation for internal controls, audits and compliance requirements.

                This traceability is essential to responsible digital processes, particularly in regulated industries and complex project organisations.

                INFORMATION SECURITY

                Assessed information security with TISAX®

                TISAX-assessed information security at Can Do

                TISAX®-assessed information security 

                Can Do has successfully completed a TISAX® (Trusted Information Security Assessment Exchange) assessment.

                TISAX is an established information security assessment mechanism, particularly in the automotive industry and its supply chains. It sets demanding requirements for handling sensitive business information.

                The assessment underlines that information security at Can Do is part of a structured information security management system, as well as a product feature.

                Current TISAX® Scope ID: S0LH92

                CLOUD & HOSTING

                Secure cloud infrastructure in Germany  

                Powered by Amazon Web Services

                Can Do uses AWS for its SaaS offering.

                Application and user data is processed in the AWS data centre in Frankfurt am Main (EU Central). Redundant systems also run within the EU Central region.

                AWS also operates to extensive international security and compliance standards. Businesses with particularly demanding requirements can run Can Do on premises or in their own private cloud infrastructure.

                AI GOVERNANCE

                AI governance beyond the black box  

                Can Do AI risk analysis (German interface)

                Businesses need more than a powerful model to use artificial intelligence professionally.

                What matters is how the following work together:

                AI technology with

                • human oversight
                • data protection
                • information security
                • access control
                • traceability
                • governance

                Can Do’s AI architecture is designed around this combination.

                Can Do helps project managers make better decisions while keeping sensitive business data under control and preserving human responsibility for decision-making.

                CAN DO AI 

                Can Do AI: learning within your organisation 

                Can Do uses several AI and machine learning methods. These include an adaptive model based on Inverse Reinforcement Learning (IRL).

                The distinctive feature: the AI learns from how people actually use the software.

                When several alternatives are available to resolve a resource bottleneck, for example, the system can learn from users’ decisions and adapt future suggestions to the way their organisation works.

                The learning models remain specific to each customer and isolated from one another.

                What the AI learns in one organisation is not transferred to another.

                Over time, the AI develops a better understanding of the organisation’s individual planning and decision-making processes, without pooling business data in a central AI model.

                SECURITY & COMPLIANCE

                Bringing the AI Act, GDPR and TISAX® together  

                Can Do – Software Made in Germany

                Trustworthy AI involves more than a single regulation.

                EU AI Act

                A framework for the safe, transparent and responsible use of artificial intelligence.

                GDPR

                Protection of personal data and clear rules for processing it.

                TISAX®

                An assessed framework for demanding information and data security requirements.

                Can Do AI Governance

                Technical and organisational principles for controlled, traceable and secure AI in project and resource management.

                This brings AI innovation and compliance together as complementary goals.

                INDUSTRY REQUIREMENTS

                Especially relevant for regulated businesses  

                Requirements for AI, data protection and information security vary by industry and use case.

                Controlled AI systems are particularly relevant in areas such as:

                Automotive & mechanical engineering
                Protecting sensitive development, project and resource data while meeting demanding requirements across complex supply chains.

                Pharma, biotech & life sciences
                Demanding requirements for governance, documentation, traceability and controlled processes.

                Chemicals & process industries
                Complex project environments with stringent security, compliance and documentation requirements.

                IT & software development
                AI-supported resource and project planning while protecting employee, project and business data.

                Use AI while staying in control  

                When adopting AI, businesses need to ask more than ‘What can it do?’ They also need to know:

                Where is our data stored?
                Who can access it?
                What data is used to train the AI?
                Is data transferred to external AI providers?
                Can we understand how results are reached?
                Who makes the final decision?
                What governance and security controls are in place? 

                Can Do has addressed these questions in its AI architecture from the outset. The result is capable AI that businesses can control, even in demanding enterprise environments.

                See trustworthy AI for project management in action 

                Want to understand how Can Do uses AI for resource planning, risk analysis and project control, and how it addresses data protection, information security and governance?

                In a personal demo, we show you Can Do’s AI features and answer questions from your IT, data protection, compliance and information security teams.

                Book a demo   Watch introduction (German)

                Frequently asked questions about AI Act Readiness, AI and compliance 

                Is Can Do certified under the EU AI Act?

                No. There is no general official ‘AI Act Ready’ certification or EU seal of approval in this form. Can Do uses ‘AI Act Readiness’ to describe how its AI architecture, development principles and governance align with the requirements and principles of the EU AI Act relevant to the software.

                The regulatory requirements that apply in practice depend, among other things, on the use case and the organisation’s role under the AI Act.

                Is our data transferred to ChatGPT or other external AI services?

                 No. Can Do’s AI models operate within each Can Do system environment and do not communicate with third-party AI systems such as ChatGPT or AWS Q for their analyses. Customer data stays within the protected environment. 

                Does Can Do AI learn from other organisations’ data?

                 No. Learning takes place within each customer’s instance. Learning models and learned patterns are not exchanged between organisations. 

                Does the AI make independent decisions about employees or projects?

                 Can Do’s AI supports users with analyses, alerts and recommended actions. People retain decision-making authority. 

                Where is cloud data stored?

                 The SaaS version of Can Do runs on AWS with servers in Frankfurt am Main. Can Do can also be deployed on premises or in your own private cloud. 

                Is Can Do GDPR-compliant?

                 Yes. Can Do is fully GDPR-compliant and takes relevant data protection requirements into account when processing and storing data. 

                Has Can Do completed a TISAX® assessment?

                Yes. Can Do GmbH has successfully completed a TISAX® assessment. The current Scope ID is S0LH92. 

                Does Can Do provide an audit trail?

                Yes. Changes and actions are recorded within the system, and processing steps are stored in a traceable way. This supports internal control, audit and compliance requirements. 

                KNOWLEDGE & INSIGHTS

                Further reading

                WHITEPAPER

                AI in Project Management

                Explore how artificial intelligence supports project and portfolio management.

                Read whitepaper

                ARTICLE · 13 APRIL 2025

                Scenario planning with Can Do

                Test alternative plans and understand their impact before changing live project data.

                Read article

                WHITEPAPER

                AI Project Management for IT & Software Development

                Explore AI-supported project planning for IT and software teams.

                Read whitepaper